Rotate first, then rewrite history. Deleting the file does nothing
git log -p -S "sk_live_" --all |headgit log -p --all -G "[0-9]{4}[- ]?[0-9]{4}[- ]?[0-9]{4}[- ]?[0-9]{4}" | grep -cE "^\+"
Get every Fix AI Slop Code episode
The code it wrote, the code it should have written and a check, for every episode
What is going on
A commit that removes a secret leaves it in every prior commit, every clone, every fork, and GitHub's cached views of deleted forks. A leaked key on GitHub or Docker Hub is tried within minutes. 64 percent of valid secrets leaked in 2022 were still valid in January 2026.
Where it bit
A personal phone number in commented-out JSX in the portfolio, in history forever. TruffleHog pulled 40 valid keys out of deleted forks in one study.
The practice
Rotate the credential first, because the scrub is cosmetic until you do. Then git filter-repo --sensitive-data-removal, force push, and a support ticket for cached views. Push protection on every public repo so it cannot happen again.
Get this check as a script you can run tonight
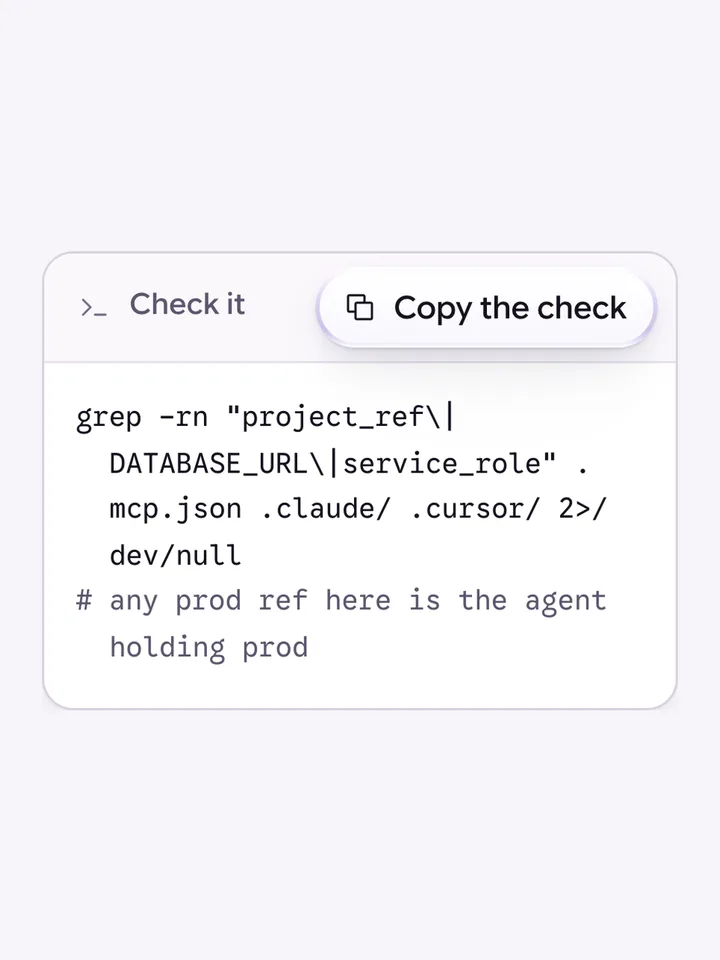
The coding agent never holds production credentials
An agent with a production database URL will sooner or later run a migration or a cleanup against it, so production secrets never enter its env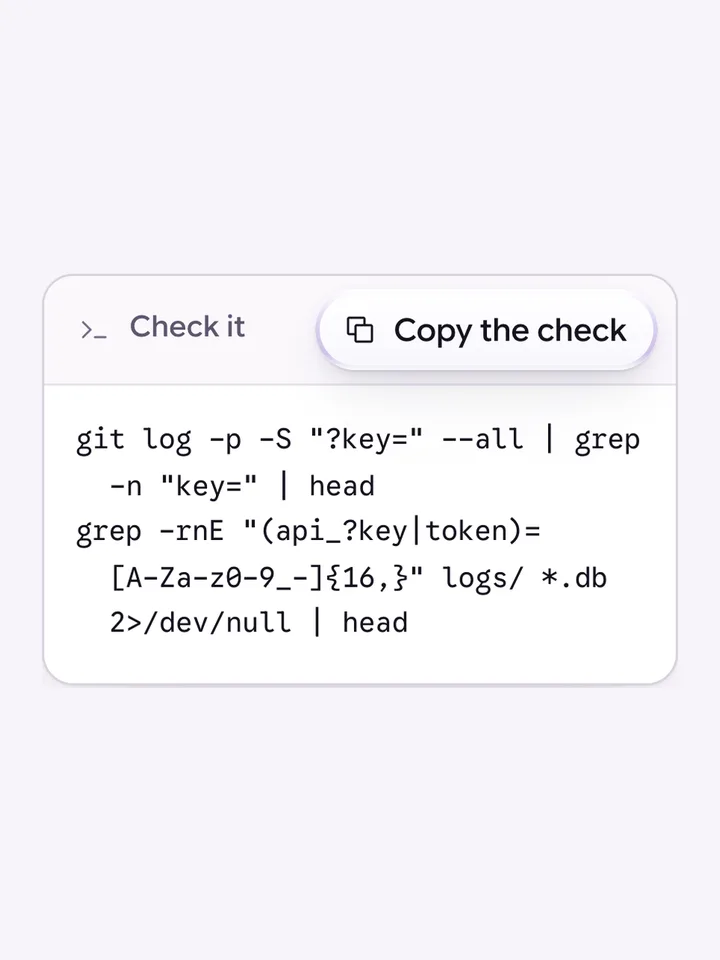
Keys go in headers, never in URLs
A URL is written to server logs, CDN logs, browser history and error trackers, so an API key in a query string is a key in five places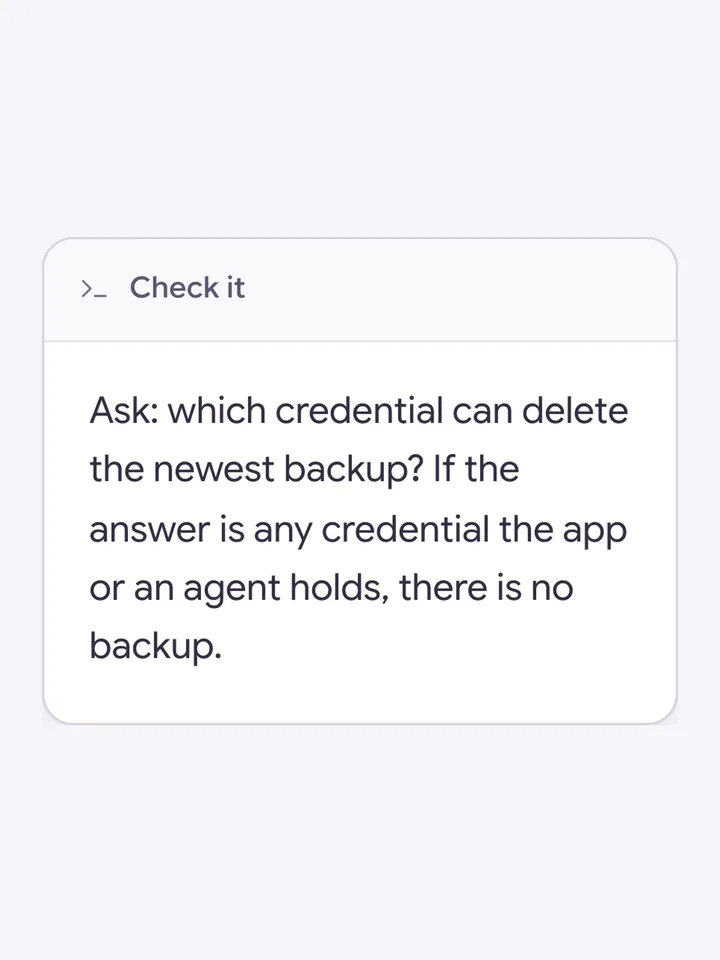
Backups the app cannot reach, and one restore you have actually done
A backup on the same account the app or an agent can delete from is not a backup, and a restore you have never run is a number you do not have
If this check came back with more than you expected, that is worth a conversation