The coding agent never holds production credentials
grep -rn "project_ref\|DATABASE_URL\| service_role" . mcp. json . claude/ . cursor/ 2>/ dev/ null# any prod ref here is the agent holding prod
Get every Fix AI Slop Code episode
The code it wrote, the code it should have written and a check, for every episode
What is going on
An agent with a production database URL will, sooner or later, run a migration, a cleanup, or a "fix" against it. Replit's agent deleted 1,206 executive records during a declared code freeze. PocketOS lost its database and its volume backups in nine seconds; the newest usable backup was three months old. A support ticket made a Supabase-MCP agent dump integration_tokens as service_role.
Where it bit
Ours: headless Claude on a root VPS with --dangerously-skip-permissions. The CLI refuses to run that way under root, and the first attempt hung on a permission prompt nobody could see. The fix that mattered was not the root check. It was giving the audit path zero tools and the screenshot judge exactly one, Read.
The practice
Agents get a dev project or a branch, read_only=true on the MCP, and prod secrets never enter their env. Destructive commands need a confirm gate that is not the agent. The permission is the tool list, not the instruction text.
Get this check as a script you can run tonight
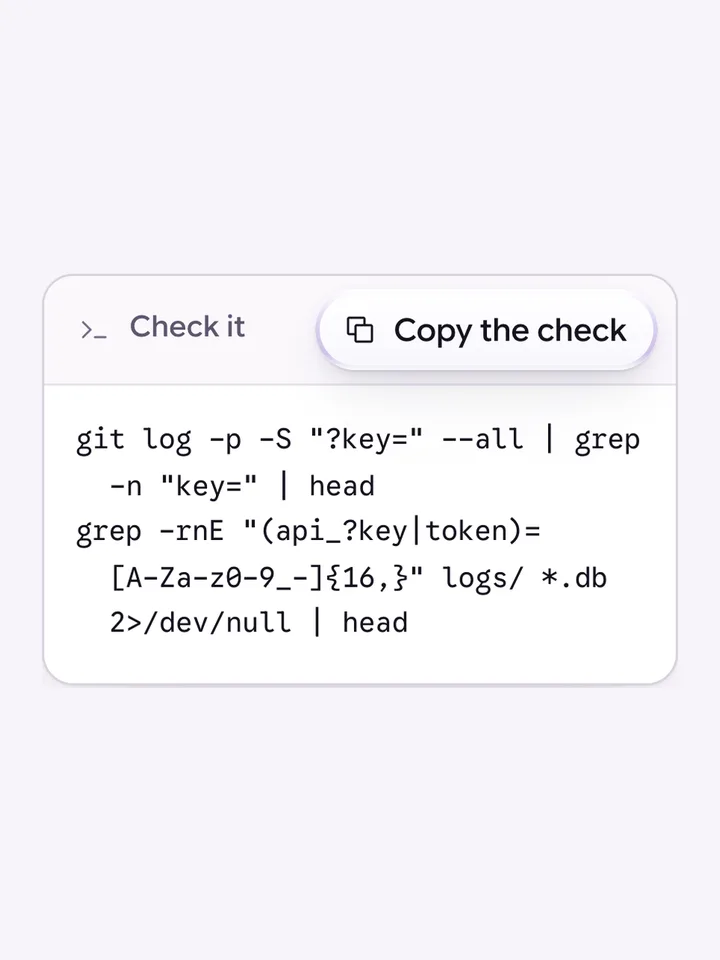
Keys go in headers, never in URLs
A URL is written to server logs, CDN logs, browser history and error trackers, so an API key in a query string is a key in five places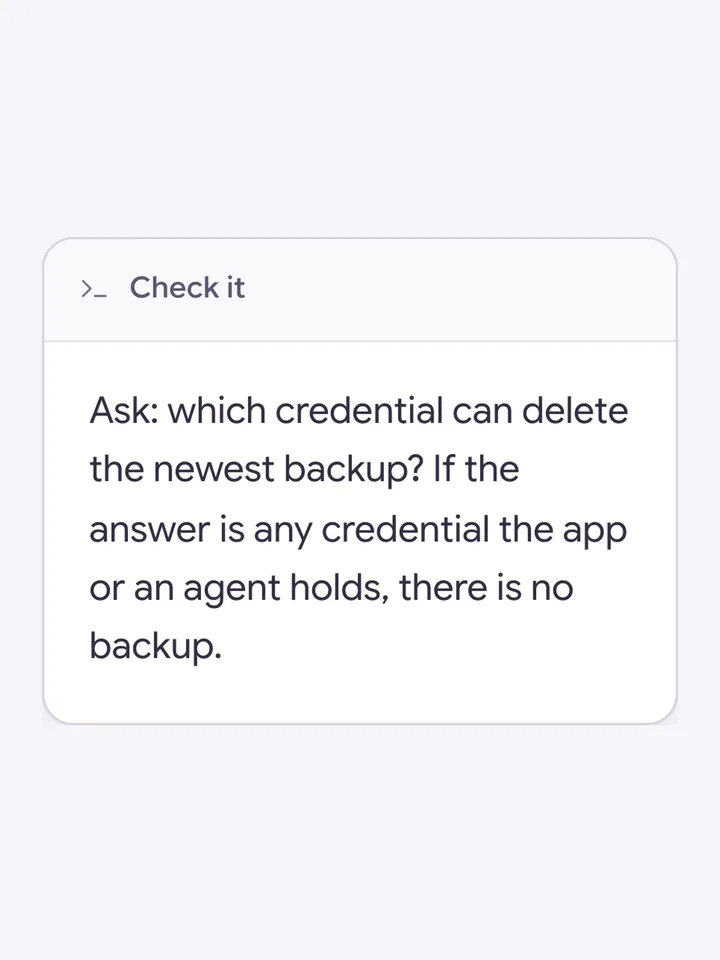
Backups the app cannot reach, and one restore you have actually done
A backup on the same account the app or an agent can delete from is not a backup, and a restore you have never run is a number you do not have 2 min read
Claude's /security-review found 31 vulnerabilities, and 5 were real
A product with four years of security work behind it ran Claude's /security-review. It reported 31 vulnerabilities. After the engineers checked each one, 5 were worth fixing
If this check came back with more than you expected, that is worth a conversation